
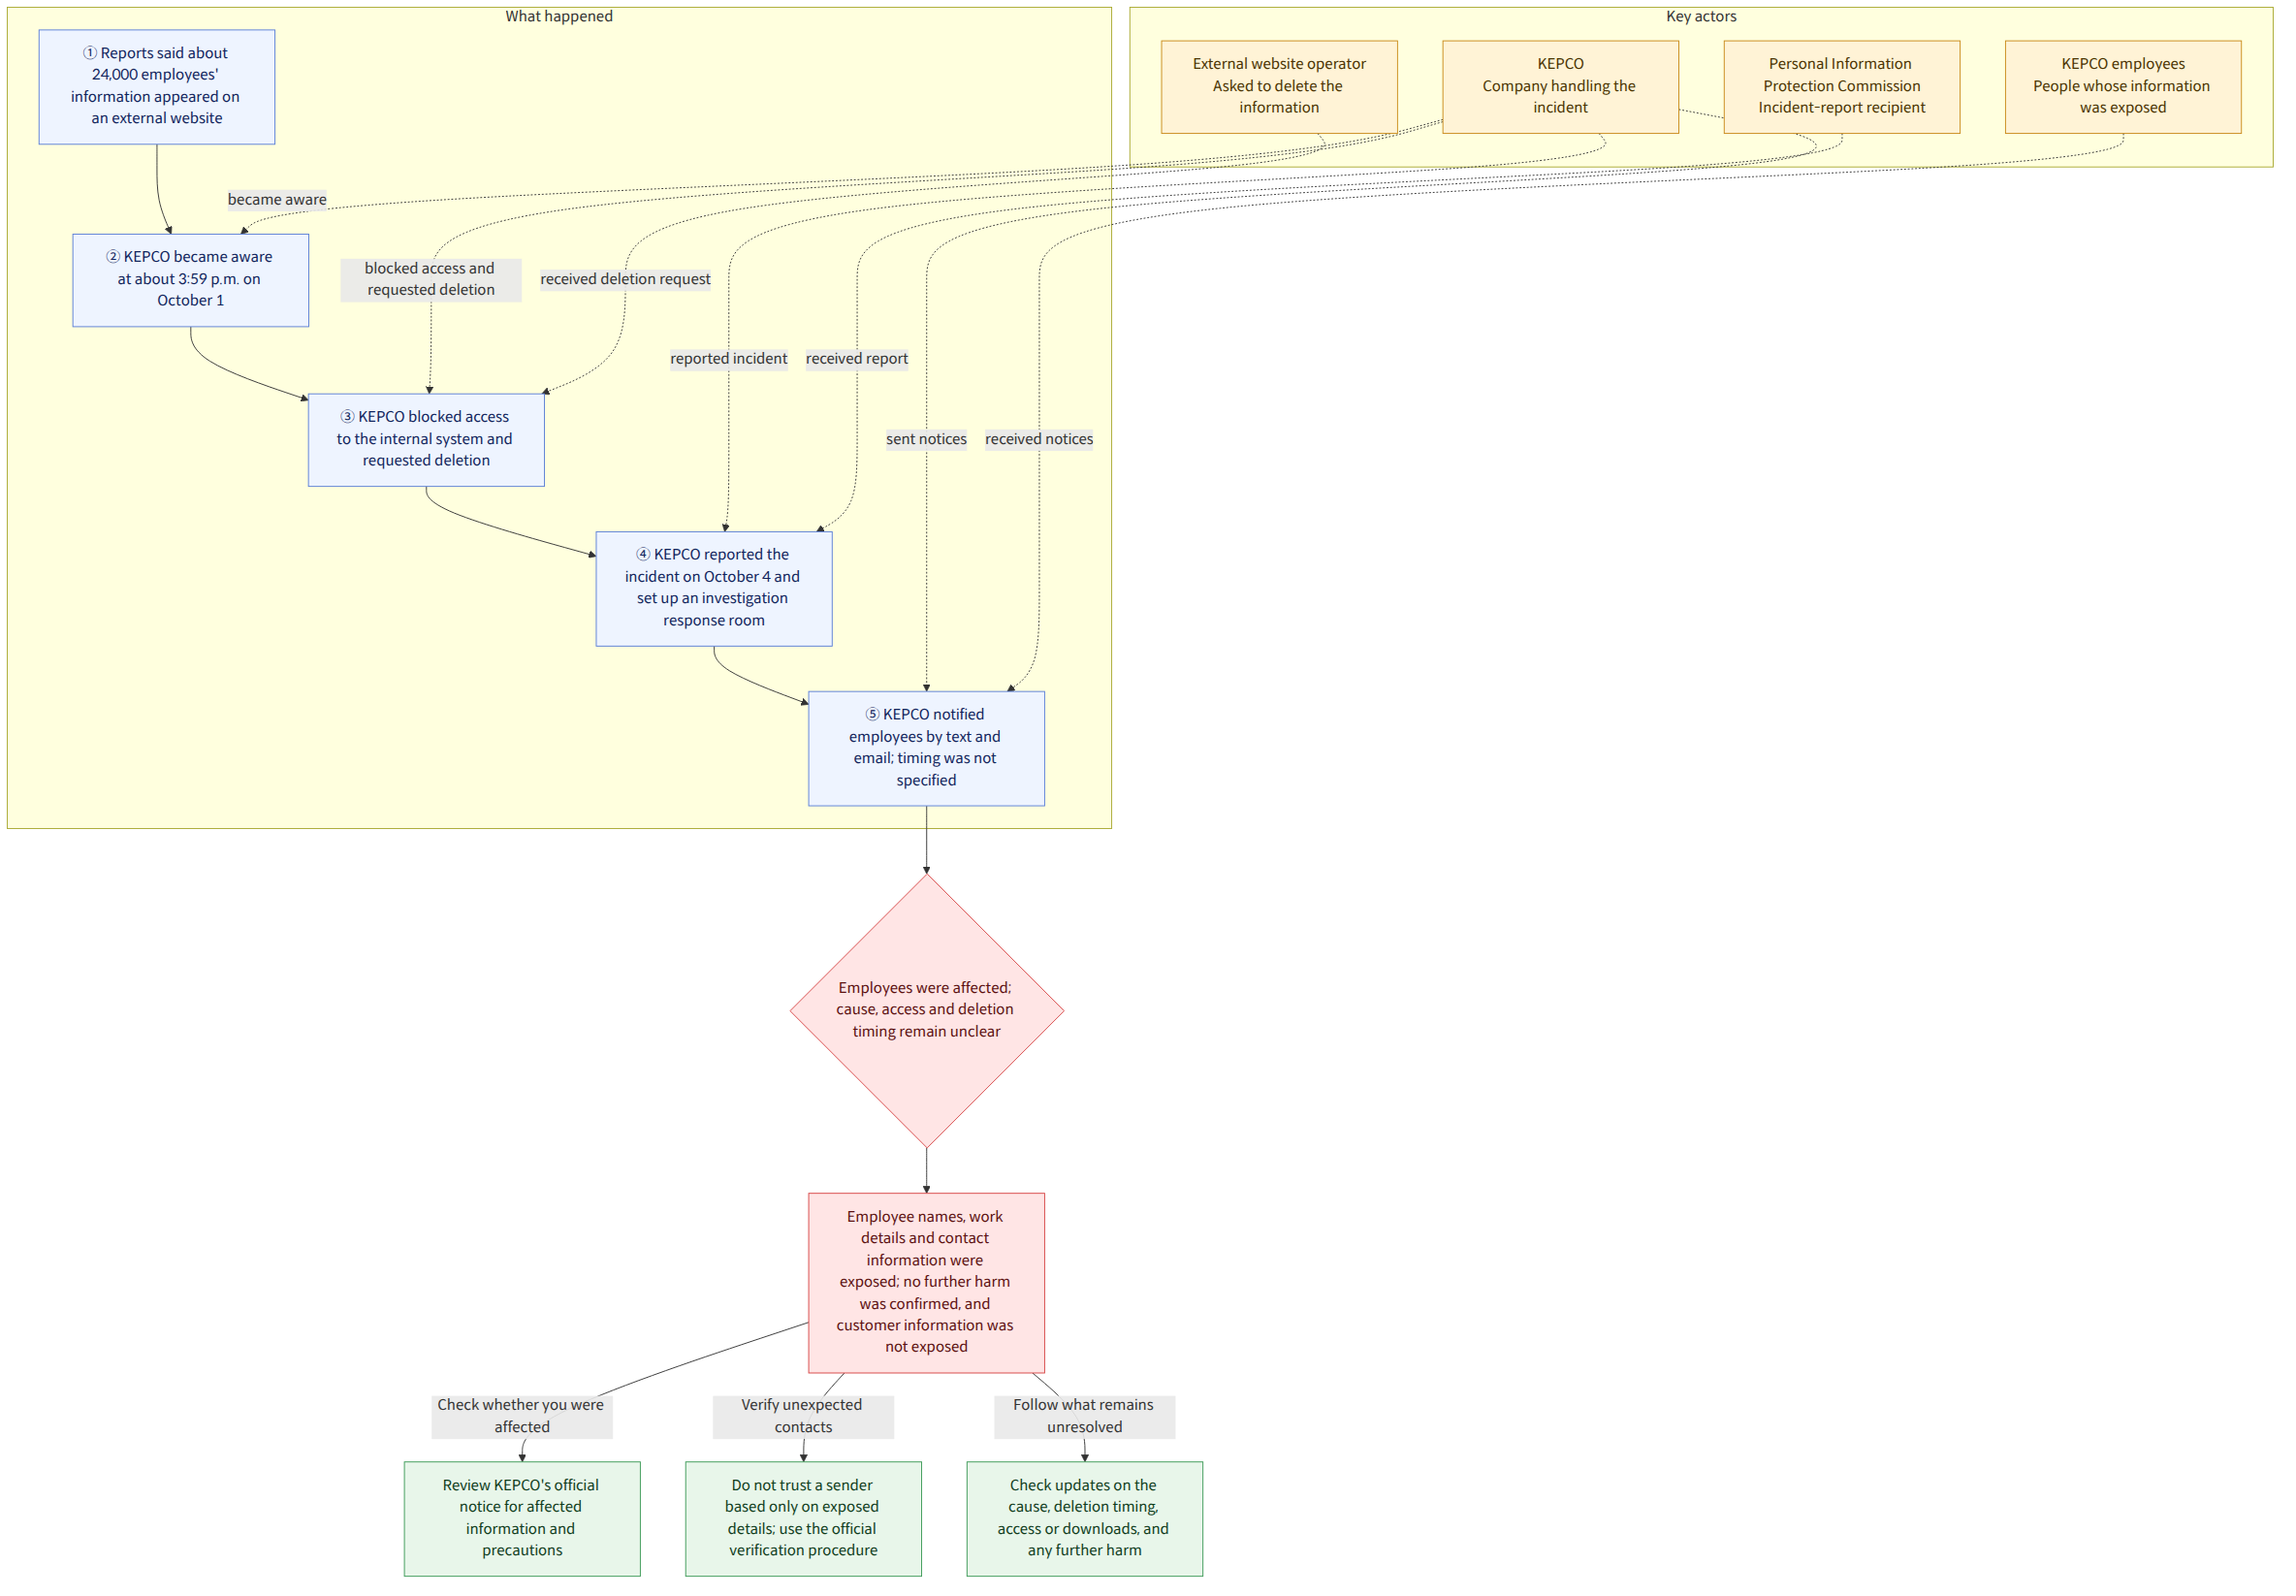
Reports say the personal information of about 24,000 employees of Korea Electric Power Corporation (한국전력공사; KEPCO) was exposed on an external website. According to KEPCO’s account as reported, the exposed information comprised seven categories: names, departments, employee ID numbers, mobile phone numbers, office phone numbers, email addresses and job titles. KEPCO said that customer information and unique identifying information such as resident registration numbers (information that uniquely identifies an individual), as well as sensitive information, were not exposed.
Background and context
KEPCO reportedly became aware of the exposure at about 3:59 p.m. on October 1. The company said it blocked access to the internal system containing employee personal information and asked the operator of the external website to delete the information.
According to reports, KEPCO reported the incident to the Personal Information Protection Commission (개인정보보호위원회) at about 1:22 p.m. on October 4 and set up an emergency response situation room with relevant agencies to investigate the circumstances. It reportedly notified employees individually by text message and email about the incident and its circumstances, and provided guidance on precautions to prevent further harm.
What this news means
KEPCO said the information was not highly sensitive data such as resident registration numbers. Still, the reported exposure of names, departments, employee ID numbers, contact details, email addresses and job titles together warrants attention. Combined, this information could enable someone to identify an employee or attempt to contact them while posing as an actual workplace associate. However, the reports provided do not say that any such further harm has actually occurred.
For example, if an employee receives a message from someone impersonating a company associate, it may be prudent not to assume that the contact is legitimate just because the sender knows the employee’s name or department. This is a precautionary interpretation based on the types of information exposed; it does not mean that any impersonation-related harm has been confirmed.
KEPCO said customer information was stored in a separate system and was not exposed. Accordingly, the reported incident directly affected employee information and should not be construed as extending to customer information.
What differs between reports
Reports differ on when the information was deleted from the website. One report said it was deleted around midnight as October 3 began, about 32 hours after KEPCO became aware of the exposure, while another said the deletion was completed around midnight on Friday. It is therefore difficult to state a single definitive deletion time or duration.
Reports also differ in how they describe the cause of the incident. One headline called it a “hacking leak,” but the article said the exact circumstances of the exposure were still under investigation. Another report said a KEPCO official was investigating the cause and believed it was unrelated to artificial intelligence. The available evidence does not allow the cause of the exposure to be determined conclusively.
What is confirmed and what remains unknown
Confirmed facts
- Reports put the number of affected employees at about 24,000.
- Seven categories of information were reportedly exposed: names, departments, employee ID numbers, mobile phone numbers, office phone numbers, email addresses and job titles.
- KEPCO said it blocked access to the internal system and asked the operator of the external website to delete the information.
- Reports said KEPCO notified employees about the incident by text message and email, and reported it to the Personal Information Protection Commission.
What remains unknown
- How and why was the information posted on the external website?
- Exactly how long was the information publicly accessible, and did anyone actually view or download it?
- What specific precautions were communicated to affected employees, and did any further harm actually occur?
What readers can check
- KEPCO employees can review the official notice from the company to see whether their information was affected and what information and precautions the notice covers.
- Be cautious about contacts that ask you to trust them based only on exposed information such as your name or department. It may help to verify the sender through the official verification procedure described in the company’s notice.
References
- Other coverage consulted: hani.co.kr
- Other coverage consulted: koreatimes.co.kr

















